Rate this post

[Mar 05, 2026] New Updated SC-200 Exam Questions 2026

Updated Free Microsoft SC-200 Test Engine Questions with 370 Q&As

The Microsoft SC-200 exam consists of multiple-choice questions, which are designed to test the candidate’s knowledge and understanding of the security operations. The questions are based on real-world scenarios, making it more practical and relevant to the industry. SC-200 exam is conducted online and can be taken from anywhere in the world, making it convenient for professionals who are working full-time.


NO.203 You have a Microsoft Sentinel workspace that contains the following Advanced Security Information Model (ASIM) parsers:
* _Im_ProcessCreate
* InProceessCreate
You create a new source-specific parser named vimProcessCreate.
You need to modify the parsers to meet the following requirements:
* Call all the ProcessCreate parsers.
* Standardize fields to the Process schema.
Which parser should you modify to meet each requirement? To answer, drag the appropriate parsers to the correct requirements. tach parser may be used once, more than once, or not at all You may need to drag the split bar between panes or scroll to view content.
NOTE Each correct selection is worth one point.

NO.204 You have an Azure subscription that is linked to a hybrid Azure AD tenant and contains a Microsoft Sentinel workspace named Sentinel1.
You need to enable User and Entity Behavior Analytics (UEBA) for Sentinel 1 and configure UEBA to use data collected from Active Directory Domain Services (AD OS).
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

NO.205 You need to implement Microsoft Sentinel queries for Contoso and Fabrikam to meet the technical requirements.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

NO.206 You have a Microsoft 365 E5 subscription that uses Microsoft Defender and an Azure subscription that uses Azure Sentinel.
You need to identify all the devices that contain files in emails sent by a known malicious email sender. The query will be based on the match of the SHA256 hash.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

NO.207 You have a Microsoft Sentine1 workspace that contains a custom workbook named Workbook1.
You need to create a visual in Workbook1 that will display the logon count for accounts that have logon event IDs of 4624 and 4634.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE Each correct selection is worth one point.

NO.208 The issue for which team can be resolved by using Microsoft Defender for Endpoint?


NO.209 You have 500 on-premises devices.
You have a Microsoft 365 E5 subscription that uses Microsoft Defender XDR.
You onboard 100 devices to Microsoft Defender XDR.
You need to identify any unmanaged on-premises devices. The solution must ensure that only specific onboarded devices perform the discovery.
What should you do first?


NO.210 You have a Microsoft Sentinel workspace that contains an Azure AD data connector.
You need to associate a bookmark with an Azure AD-related incident.
What should you do? To answer, drag the appropriate blades to the correct tasks. Each blade may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content NOTE: Each correct selection is worth one point.

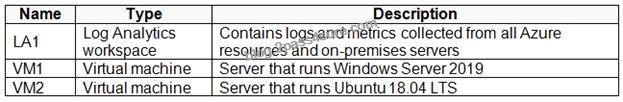
NO.211 Your on-premises network contains a Hyper-V cluster. The cluster contains the virtual machines shown in the following table.

You have a Microsoft Sentinel workspace named SW1.
You have a data collection rule (OCR) that has the following configurations:
* Name: DCR1
* Destination: SW1
* Platform type: All
* Data collection endpoint: None
* Data source: Windows event logs, Linux syslog
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

NO.212 From Azure Sentinel, you open the Investigation pane for a high-severity incident as shown in the following exhibit.

Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.

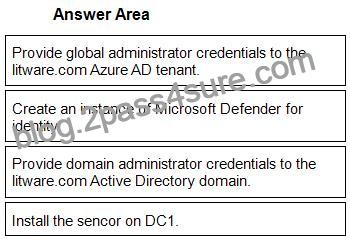
NO.213 You have an Azure subscription. The subscription contains 10 virtual machines that are onboarded to Microsoft Defender for Cloud.
You need to ensure that when Defender for Cloud detects digital currency mining behavior on a virtual machine, you receive an email notification. The solution must generate a test email.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
NO.214 You have the following SQL query.

NO.215 You are investigating an incident by using Microsoft 365 Defender.
You need to create an advanced hunting query to count failed sign-in authentications on three devices named CFOLaptop. CEOLaptop, and COOLaptop.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE Each correct selection is worth one point

NO.216 You have a Microsoft 365 E5 subscription that uses Microsoft Defender XDR.
You are implementing a deception rule.
You need to provide a custom lure file.
For the custom lure, you set Planting path to HOME.
Which types of files can you use for the custom lure, and in which home directory should the file be located on a device? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

NO.217 You have a Microsoft Sentinel workspace.
You plan to visualize data from Microsoft SharePoint Online and OneDrive sites.
You need to create a KQL query for the visual. The solution must meet the following requirements:
* Select all workloads as a single operation.
* Include two parameters named Operations and Users.
* In the results, exclude empty values for the site URLs.
How should you complete the query? To answer, select the appropriate options in the answer area. NOTE:
Each correct selection is worth one point.

NO.218 You have a Microsoft 365 subscription
You need to identify all the security principals that submitted requests to change or delete groups. How should you complete the KQL query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

NO.219 You have a Microsoft Sentinel workspace named sws1.
You need to create a hunting query to identify users that list storage keys of multiple Azure Storage accounts.
The solution must exclude users that list storage keys for a single storage account.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

NO.220 You have an Azure subscription that uses Microsoft Sentinel.
You detect a new threat by using a hunting query.
You need to ensure that Microsoft Sentinel automatically detects the threat. The solution must minimize administrative effort.
What should you do?


NO.221 You have an Azure subscription that contains a resource group named RG1. RG1 contains a Microsoft Sentinel workspace. The subscription is linked to a Microsoft Entra tenant that contains a user named User1.
You need to ensure that User1 can deploy and customize Microsoft Sentine1 workbook templates. The solution must follow the principle of least privilege.
Which role should you assign to User1 for RG1?


NO.222 You have an Azure subscription.
You need to delegate permissions to meet the following requirements:
* Enable and disable advanced features of Microsoft Defender for Cloud.
* Apply security recommendations to a resource.
The solution must use the principle of least privilege.
Which Microsoft Defender for Cloud role should you use for each requirement? To answer, drag the appropriate roles to the correct requirements. Each role may be used once, mote than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.

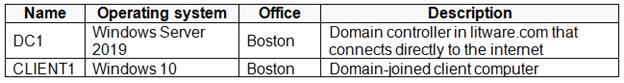
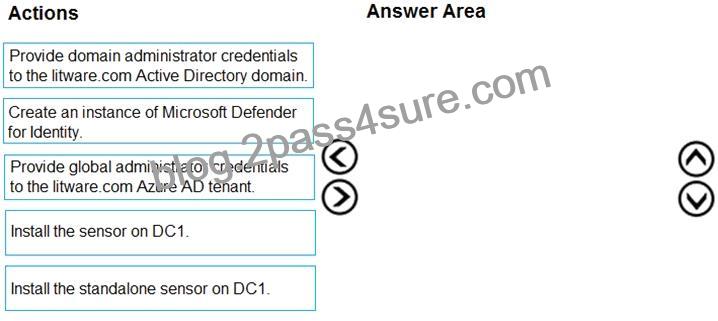
NO.223 You need to configure DC1 to meet the business requirements.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.

NO.224 You have a Microsoft Sentinel workspace
You develop a custom Advanced Security information Model (ASIM) parser named Parser1 that produces a schema named Schema1.
You need to validate Schema1.
How should you complete the command? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

NO.225 You have a Microsoft Sentinel workspace named sws1.
You need to create a hunting query to identify users that list storage keys of multiple Azure Storage accounts. The solution must exclude users that list storage keys for a single storage account.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

NO.226 You have an Azure subscription that has Azure Defender enabled for all supported resource types.
You create an Azure logic app named LA1.
You plan to use LA1 to automatically remediate security risks detected in Defenders for Cloud.
You need to test LA1 in Defender for Cloud.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.


Try 100% Updated SC-200 Exam Questions [2026]: https://www.2pass4sure.com/Microsoft-Certified-Security-Operations-Analyst-Associate/SC-200-actual-exam-braindumps.html


Related Links: myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt www.stes.tyc.edu.tw myportal.utt.edu.tt