Rate this post

[2022] Use Valid New SC-200 Questions – Top choice Help You Gain Success

SC-200 Exam Practice Materials Collection

Microsoft SC-200 Exam Syllabus Topics:

Topic Details
Topic 1
  • Investigate Azure Defender alerts and incidents
  • Configure device attack surface reduction rules
Topic 2
  • Mitigate threats using Azure Defender
  • Identify and remediate security risks using Secure Score
Topic 3
  • Identify and remediate security risks related to sign-in risk policies
  • Identify data sources to be ingested for Azure Sentinel
Topic 4
  • Design and Configure Windows Events collections
  • Manage data loss prevention policy alerts
Topic 5
  • Manage user data discovered during an investigation
  • Assess and recommend insider risk policies
Topic 6
  • Detect, investigate, respond, and remediate identity threats
  • Configure and manage custom detections and alerts
Topic 7
  • Design and configure an Azure Defender implementation
  • Configure automated responses in Azure Security Center
Topic 8
  • Identify and remediate security risks related to Conditional Access events
  • manage data retention, alert notification, and advanced features
Topic 9
  • Identify and remediate security risks related to Azure Active Directory
  • Remediate incidents by using Azure Defender recommendations

Exam SC-200: Microsoft Security Operations Analyst

The content of this exam was updated on July 23, 2021.

The Microsoft Security Operations Analyst collaborates with organizational stakeholders to secure information technology systems for the organization. Their goal is to reduce organizational risk by rapidly remediating active attacks in the environment, advising on improvements to threat protection practices, and referring violations of organizational policies to appropriate stakeholders.

Responsibilities include threat management, monitoring, and response by using a variety of security solutions across their environment. The role primarily investigates, responds to, and hunts for threats using Microsoft Azure Sentinel, Azure Defender, Microsoft 365 Defender, and third-party security products. Since the Security Operations Analyst consumes the operational output of these tools, they are also a critical stakeholder in the configuration and deployment of these technologies.

Part of the requirements for: Microsoft Certified: Security Operations Analyst Associate

Download exam skills outline


QUESTION 20
HOTSPOT
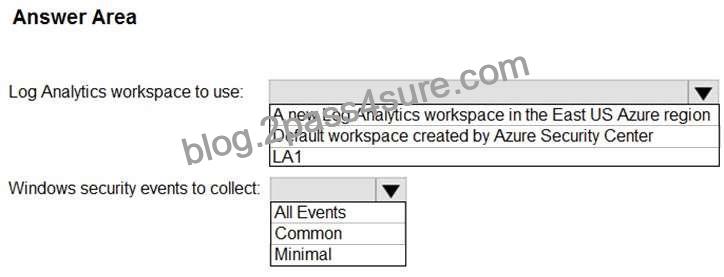
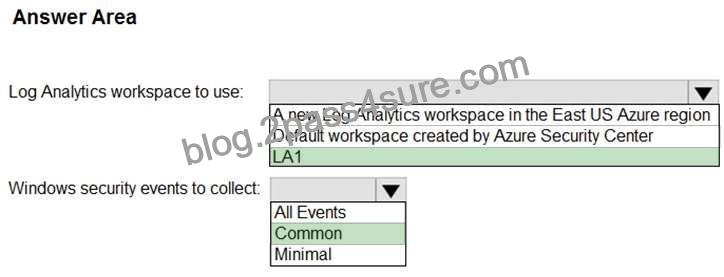
You need to configure the Azure Sentinel integration to meet the Azure Sentinel requirements.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
QUESTION 21
You create a new Azure subscription and start collecting logs for Azure Monitor.
You need to configure Azure Security Center to detect possible threats related to sign-ins from suspicious IP addresses to Azure virtual machines. The solution must validate the configuration.
Which three actions should you perform in a sequence? To answer, move the appropriate actions from the list of action to the answer area and arrange them in the correct order.

QUESTION 22
The issue for which team can be resolved by using Microsoft Defender for Endpoint?


QUESTION 23
You use Azure Sentinel.
You need to receive an immediate alert whenever Azure Storage account keys are enumerated.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.


QUESTION 24
You implement Safe Attachments policies in Microsoft Defender for Office 365.
Users report that email messages containing attachments take longer than expected to be received.
You need to reduce the amount of time it takes to deliver messages that contain attachments without compromising security. The attachments must be scanned for malware, and any messages that contain malware must be blocked.
What should you configure in the Safe Attachments policies?


QUESTION 25
You plan to connect an external solution that will send Common Event Format (CEF) messages to Azure Sentinel.
You need to deploy the log forwarder.
Which three actions should you perform in sequence? To answer, move the appropriate actions form the list of actions to the answer area and arrange them in the correct order.

QUESTION 26
You create a new Azure subscription and start collecting logs for Azure Monitor.
You need to configure Azure Security Center to detect possible threats related to sign-ins from suspicious IP addresses to Azure virtual machines. The solution must validate the configuration.
Which three actions should you perform in a sequence? To answer, move the appropriate actions from the list of action to the answer area and arrange them in the correct order.

QUESTION 27
Your company uses Azure Sentinel.
A new security analyst reports that she cannot assign and dismiss incidents in Azure Sentinel. You need to resolve the issue for the analyst. The solution must use the principle of least privilege. Which role should you assign to the analyst?


QUESTION 28
HOTSPOT
You need to implement Azure Defender to meet the Azure Defender requirements and the business requirements.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:

QUESTION 29
You create an Azure subscription named sub1.
In sub1, you create a Log Analytics workspace named workspace1.
You enable Azure Security Center and configure Security Center to use workspace1.
You need to collect security event logs from the Azure virtual machines that report to workspace1.
What should you do?


QUESTION 30
You need to configure DC1 to meet the business requirements.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.

QUESTION 31
Your company uses Azure Sentinel.
A new security analyst reports that she cannot assign and dismiss incidents in Azure Sentinel. You need to resolve the issue for the analyst. The solution must use the principle of least privilege. Which role should you assign to the analyst?


QUESTION 32
You need to implement the Azure Information Protection requirements. What should you configure first?


QUESTION 33
You have a Microsoft 365 subscription that uses Microsoft Defender for Office 365.
You have Microsoft SharePoint Online sites that contain sensitive documents. The documents contain customer account numbers that each consists of 32 alphanumeric characters.
You need to create a data loss prevention (DLP) policy to protect the sensitive documents.
What should you use to detect which documents are sensitive?


QUESTION 34
You have an existing Azure logic app that is used to block Azure Active Directory (Azure AD) users. The logic app is triggered manually.
You deploy Azure Sentinel.
You need to use the existing logic app as a playbook in Azure Sentinel. What should you do first?


QUESTION 35
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You are configuring Microsoft Defender for Identity integration with Active Directory.
From the Microsoft Defender for identity portal, you need to configure several accounts for attackers to exploit.
Solution: From Entity tags, you add the accounts as Honeytoken accounts.
Does this meet the goal?


QUESTION 36
You need to create the analytics rule to meet the Azure Sentinel requirements.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

QUESTION 37
DRAG DROP
You need to add notes to the events to meet the Azure Sentinel requirements.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of action to the answer area and arrange them in the correct order.
Select and Place:

QUESTION 38
You use Azure Sentinel.
You need to receive an immediate alert whenever Azure Storage account keys are enumerated.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.


QUESTION 39
You have a playbook in Azure Sentinel.
When you trigger the playbook, it sends an email to a distribution group.
You need to modify the playbook to send the email to the owner of the resource instead of the distribution group.
What should you do?


QUESTION 40
Your company deploys the following services:
* Microsoft Defender for Identity
* Microsoft Defender for Endpoint
* Microsoft Defender for Office 365
You need to provide a security analyst with the ability to use the Microsoft 365 security center. The analyst must be able to approve and reject pending actions generated by Microsoft Defender for Endpoint. The solution must use the principle of least privilege.
Which two roles should assign to the analyst? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.


QUESTION 41
You need to create the test rule to meet the Azure Sentinel requirements.
What should you do when you create the rule?


QUESTION 42
You have an Azure Sentinel deployment.
You need to query for all suspicious credential access activities.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.


Skills measured

  • The content of this exam was updated on July 23, 2021. Please download the exam skills outline below to see what changed.
  • Mitigate threats using Azure Defender (25-30%)
  • Mitigate threats using Microsoft 365 Defender (25-30%)
  • Mitigate threats using Azure Sentinel (40-45%)


Maximum Grades By Making ready With SC-200 Dumps: https://www.2pass4sure.com/Microsoft-Certified-Security-Operations-Analyst-Associate/SC-200-actual-exam-braindumps.html


Related Links: www.stes.tyc.edu.tw www.stes.tyc.edu.tw www.stes.tyc.edu.tw www.stes.tyc.edu.tw www.stes.tyc.edu.tw www.stes.tyc.edu.tw