Rate this post

New (2023) Download free SY0-601 PDF for CompTIA Practice Tests

100% Free SY0-601 Files For passing the exam Quickly

CompTIA SY0-601: Target Audience

The candidates for this exam are the IT specialists looking to validate their information security skills and knowledge. The test is designed for those individuals who want to take up the job roles in the field of cybersecurity and need the CompTIA Security+ certification to boost their resume and increase their chance of getting a desired position.


NO.147 Select the appropriate attack and remediation from each drop-down list to label the corresponding attack with its remediation.
INSTRUCTIONS
Not all attacks and remediation actions will be used.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.

NO.148 Two organizations plan to collaborate on the evaluation of new SIEM solutions for their respective companies.
A combined effort from both organizations’ SOC teams would speed up the effort. Which of the following can be written to document this agreement?


NO.149 A security analyst receives an alert from the company’s SIEM that anomalous activity is coming from a local source IP address of 192.168.34.26. The Chief Information Security Officer asks the analyst to block the originating source. Several days later another employee opens an internal ticket stating that vulnerability scans are no longer being performed properly. The IP address the employee provides is 192.168.34.26. Which of the following describes this type of alert?


NO.150 A user downloaded an extension for a browser, and the uses device later became infected. The analyst who is investigating the incident saw various logs where the attacker was hiding activity by deleting data The following was observed running:

Which of the following is the malware using to execute the attack?


NO.151 A security manager runs Nessus scans of the network after every maintenance window. Which of the following is the security manger MOST likely trying to accomplish?


NO.152 The Chief Executive Officer announced a new partnership with a strategic vendor and asked the Chief Information Security Officer to federate user digital identities using SAML-based protocols. Which of the following will this enable?


NO.153 Which of the following allows for functional test data to be used in new systems for testing and training purposes to protect the read data?


NO.154 The website http://companywebsite.com requires users to provide personal Information, Including security question responses, for registration.
Which of the following would MOST likely cause a data breach?


NO.155 Which of the following utilize a subset of real data and are MOST likely to be used to assess the features and functions of a system and how it interacts or performs from an end user’s perspective against defined test cases? (Select TWO).


NO.156 A security analyst needs to determine how an attacker was able to use User3 to gain a foothold within a company’s network. The company’s lockout policy requires that an account be locked out for a minimum of 15 minutes after three unsuccessful attempts. While reviewing the log files, the analyst discovers the following:

Which of the following attacks MOST likely occurred?


NO.157 A manufacturing company has several one-off legacy information systems that cannot be migrated to a newer OS due to software compatibility issues. The Oss are still supported by the vendor, but the industrial software is no longer supported. The Chief Information Security Officer (CISO) has created a resiliency plan for these systems that will allow OS patches to be installed in a non-production environment, while also creating backups of the systems for recovery. Which of the following resiliency techniques will provide these capabilities?


NO.158 A company has drafted an insider-threat policy that prohibits the use of external storage devices.
Which of the following would BEST protect the company from data exfiltration via removable media?


NO.159 A company labeled some documents with the public sensitivity classification. This means the documents can be accessed by?


NO.160 A forensics investigator is examining a number of unauthorized payments the were reported on the company’s website. Some unusual log entries show users received an email for an unwanted mailing list and clicked on a link to attempt to unsubscribe. One of the users reported the email to the phishing team, and the forwarded email revealed the link to be:

Which of the following will the forensics investigator MOST likely determine has occurred?


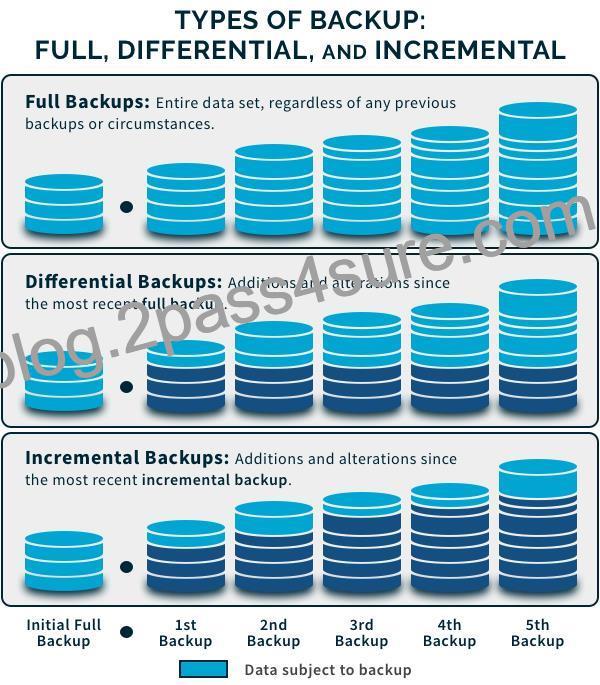
NO.161 A systems administrator is considering different backup solutions for the IT infrastructure. The company is looking for a solution that offers the fastest recovery time while also saving the most amount of storage used to maintain the backups. Which of the following recovery solutions would be the BEST option to meet these requirements?


NO.162 A user contacts the help desk to report the following:
– Two days ago, a pop-up browser window prompted the user for a name
and password after connecting to the corporate wireless SSID. This had
never happened before, but the user entered the information as
requested.
– The user was able to access the Internet but had trouble accessing
the department share until the next day.
– The user is now getting notifications from the bank about
unauthorized transactions.
Which of the following attack vectors was MOST likely used in this scenario?


NO.163 A company was compromised, and a security analyst discovered the attacker was able to get access to a service account. The following logs were discovered during the investigation:

Which of the following MOST likely would have prevented the attacker from learning the service account name?


NO.164 The chief compliance officer from a bank has approved a background check policy for all new hires. Which of the following is the policy MOST likely protecting against?


NO.165 Which of the following function as preventive, detective, and deterrent controls to reduce the risk of physical theft? (Select TWO).


NO.166 A security engineer needs to create a network segment that can be used for servers that require connections from untrusted networks When of the following should the engineer implement?


NO.167 Leveraging the information supplied below, complete the CSR for the server to set up TLS (HTTPS)
* Hostname: ws01
* Domain: comptia.org
* IPv4: 10.1.9.50
* IPV4: 10.2.10.50
* Root: home.aspx
* DNS CNAME:homesite.
Instructions:
Drag the various data points to the correct locations within the CSR. Extension criteria belong in the let hand column and values belong in the corresponding row in the right hand column.

NO.168 A security analyst is reviewing the following attack log output:
Which of the following types of attacks does this MOST likely represent?


Implementation (25%)

  • Implement certain secure network designs;
  • In a given scenario, implement account and identity management controls;
  • In a given scenario, apply a cybersecurity solution for Cloud;
  • In a given scenario, configure and install wireless security settings;
  • Implement a secure mobile solution;
  • In a given scenario, implement PKI (Public Key Infrastructure).
  • Implement application or host security solutions;
  • In a given scenario, implement specific secure protocols;


SY0-601 Premium Exam Engine – Download Free PDF Questions: https://www.2pass4sure.com/CompTIA-Security/SY0-601-actual-exam-braindumps.html


Related Links: www.stes.tyc.edu.tw www.stes.tyc.edu.tw fortunetelleroracle.com www.stes.tyc.edu.tw www.stes.tyc.edu.tw www.stes.tyc.edu.tw